In this article…
On October 21, 2026, the PHP project released new versions of PHP to address a couple of critical vulnerabilities discovered in the software. They strongly encouraged everyone using PHP — about 70% of the sites on the internet — to update immediately, or face the prospect of attackers seizing control of unprotected servers.
Since the announcement, we’ve had a few security-conscious customers reach out to see if our software is affected. The short answer is no, we’re not vulnerable, but let’s dig into the details below.

Is your software impacted by PHP2Shell?
No. The pair of vulnerabilities, called PHP2Shell, only affect PHP. And since none of our products embed or borrow components from PHP, they’re all in the clear.
What about AlwaysUp Web Service? Does it use PHP?
Even though AlwaysUp Web Service serves web pages and is accessible from your browser, it’s not impacted by the bugs. That’s because it uses its own, internally developed networking code — not PHP.
Does your website use PHP? If yes, has it been patched?
Like the majority of the world’s websites, ours rely on PHP too. Our servers were vulnerable to PHP2Shell.
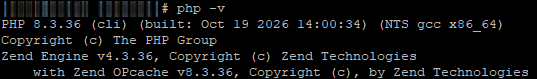
So we moved quickly to fix them. The team paused and patched all our machines on the evening of October 21, and only approved versions of PHP are running today:
How does your company respond to critical security issues like this?
As part of our information security program, we make it a point to apply operating system patches on a regular basis.
In general:
- Patches to fix critical vulnerabilities are applied as soon as possible — automatically if possible and usually within 30 days.
And for truly exceptional threats like PHP2Shell, our goal is to take action within 24 hours of a fix becoming available.
- On Linux, high, medium and low vulnerabilities are addressed as part of quarterly updates.
- We update Windows machines at least monthly (after Patch Tuesday).
Stay safe!